Before you sign: is this the real app, the real contract, and the real recipient?
HexFence is a pre-sign firewall for Ethereum. It verifies the website and contracts against the developer's signed release (the Pramaan layer), explains the request in English, हिन्दी and मराठी, and stops payments to lookalike addresses. A Safe Guard enforces the recipient rule on-chain, so a lying screen cannot override it.
Three questions, one verdict
Each answer is a row in the review window that opens before your wallet does. The worst row wins; unknown is never shown as green.
Is this the real app?
The site's files are hashed and compared with a release the developer signed and anchored on ENS behind a timelock. One changed byte turns it red and holds the signature.
Is this the real contract?
The deployed bytecode and the proxy's current implementation must match the release. A queued or executed upgrade to unlisted code is flagged.
Is this the real recipient?
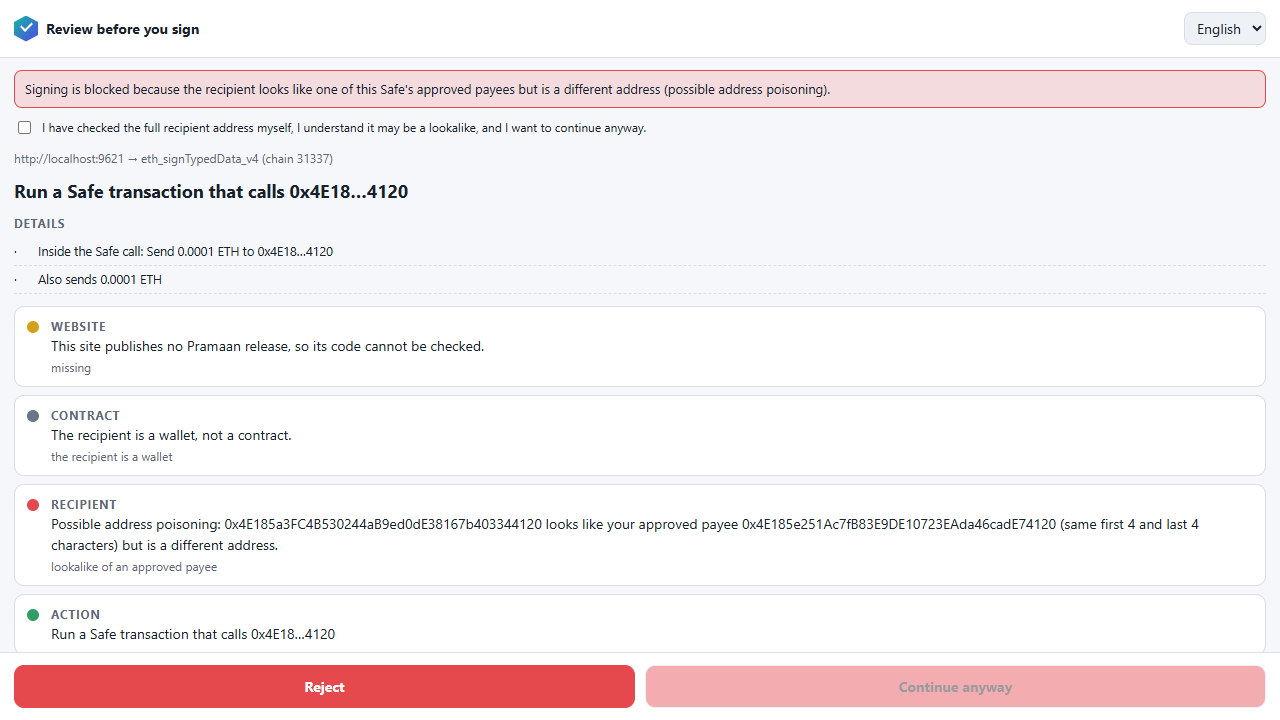
A payment to an address that shares the first 4 and last 4 characters with an approved payee (address poisoning) is red. The HexFence Guard on the Safe refuses it on-chain.
Try it now (no install)
Live on the Sepolia testnet. No real funds.
HexFence Pay
Check a Safe payment against its approved payees before signing. Try the lookalike 0x4E185a3FC4B530244aB9ed0dE38167b403344120: red "Possible address poisoning".
Evidence explorer
Real address-poisoning patterns from Ethereum mainnet, published openly on Arkiv and re-checkable on chain. Status is always "suspected".
Open the explorer →Guided demo
Five steps: the attack, the lookalike, the Guard, the three verdicts, and the on-chain refusal.
Open the guided demo →The extension: all checks in one window
One Chrome/Edge extension combines both layers. It intercepts the wallet request on any site, fails closed, and shows the five rows above.
Live demo dApps (Sepolia)
Three apps published with signed releases on Sepolia. Open them with the extension installed and MetaMask on Sepolia.
VaultLab
A vault whose bug was found, exploited and fixed in a sandbox; the proof is published with the release.
Open VaultLab →MirrorYield
An honest contract. If the website's JavaScript is changed, the extension turns red and holds the signature.
Open MirrorYield →PermitMarket
"One-click buying" is an unlimited approval; the extension explains it as high risk in three languages.
Open PermitMarket →On-chain pieces (Sepolia)
HexFence Guard v1 (no owner, no upgrade path): 0xA061fB511D69e5c92E50E3BE5c789472d6f19748 · source on Etherscan
Demo Safe: 0x3BCc3969713778F3Ed26AE1490529eeBAD43FbD5 · recorded lookalike payment refused by the Guard: transaction
Each demo app's release record lives in ENS behind a timelock; anyone can verify it with the extension or pramaan verify <url>.